

AutomoxAutomox

Suspend Bitlocker Encryption or Decrypt Drives

bwright
July 10, 2024 at 5:07 pm UTC
#Worklets#automox#bitlocker

I was able to successfully use the “Enforce Bitlocker Encryption” worklet on a few test machines.

However, I am curious if anyone knows a way to use Automox to suspend encryption in order to run updates or how to simply decrypt drives with a worklet.

The idea of encrypting drives with a worklet is helpful, but manually suspending the encryption and decrypting the devices takes a lot of work.

This discussion is archived and closed to replies. Continue it in the Automox Community Slack.

Discuss on Slack
Replies (1)

MarkH-AutomoxJuly 10, 2024
#1

Hi Bwright,

I took the Evaluation code from the Bitlocker Compliance check worklet Catalog template and flipped the compliance exit codes. There are a few lines that can be stripped out to make this shorter:

powershell84 lines
<#
    Usage:
    There is only one variable to be modified in this worklet.

    $maxSystemtype: Set this variable to limit the maximum PCSystemType to evaluate. Currently the script is set
    to a value of 3 with will exclude devices with a PCSystemType higher than a workstation (ie:Servers). If you prefer
    to run this evaluation against all devices, then a value of '8' should be specified. Refer to the list below for
    reference and change $masSystemtype as needed.

    PCSystemType
    0 = Unknown
    1 = Desktop
    2 = Mobile
    3 = Workstation
    4 = Enterprise Server
    5 = SOHO Server
    6 = Appliance PC
    7 = Performance Server
    8 = Maximum

.EXAMPLE
    $maxSystemtype = '3'
.LINK
    https://docs.microsoft.com/en-us/dotnet/api/microsoft.powershell.commands.pcsystemtype?view=powershellsdk-1.1.0
.NOTES
    Author: Tony Wiese
    Date: March 19, 2021
#>

####### EDIT WITHIN THIS BLOCK #######
$maxSystemtype = '3'
######################################

$getSystype = (Get-CimInstance -ClassName Win32_ComputerSystem).PCSystemType

# Exit if systemtype is higher than $maxSystemtype
if ($getSystype -gt $maxSystemtype)
{
    Write-Output "Device Excluded"
    Exit 0
}

#Get BitLocker status for All Drives
try
{
    $encryption = Get-BitLockerVolume -ErrorAction Stop
}
catch
{
    Exit 1
}

# Count Drives and initialize lists for later output
$numDrives = $encryption.Count
$encCount = 0
$encrypted = @()
$unencrypted = @()

# Loop through each drive and see if it is Protected or Not
# Add to the appropriate list, Encrypted or Unencrypted
foreach ($drive in $encryption)
{
    $encStatus = $drive.ProtectionStatus
    $encInProgress = $drive.VolumeStatus
    if (($encStatus -match 'On') -or ($encInProgress -match "EncryptionInProgress"))
    {
        $encrypted += $drive.MountPoint
        $encCount++
    }
    else
    {
        $unencrypted += $drive.MountPoint
    }
}

# Determine Compliant based on if the number of Encrypted
# Drives matches the number of Total Drives
if ($encCount -eq $numDrives)
{
    Write-Output "Device has Bitlocker enabled"
    Exit 1
}
Write-Output "Device does NOT have bitlocker enabled"
Exit 0

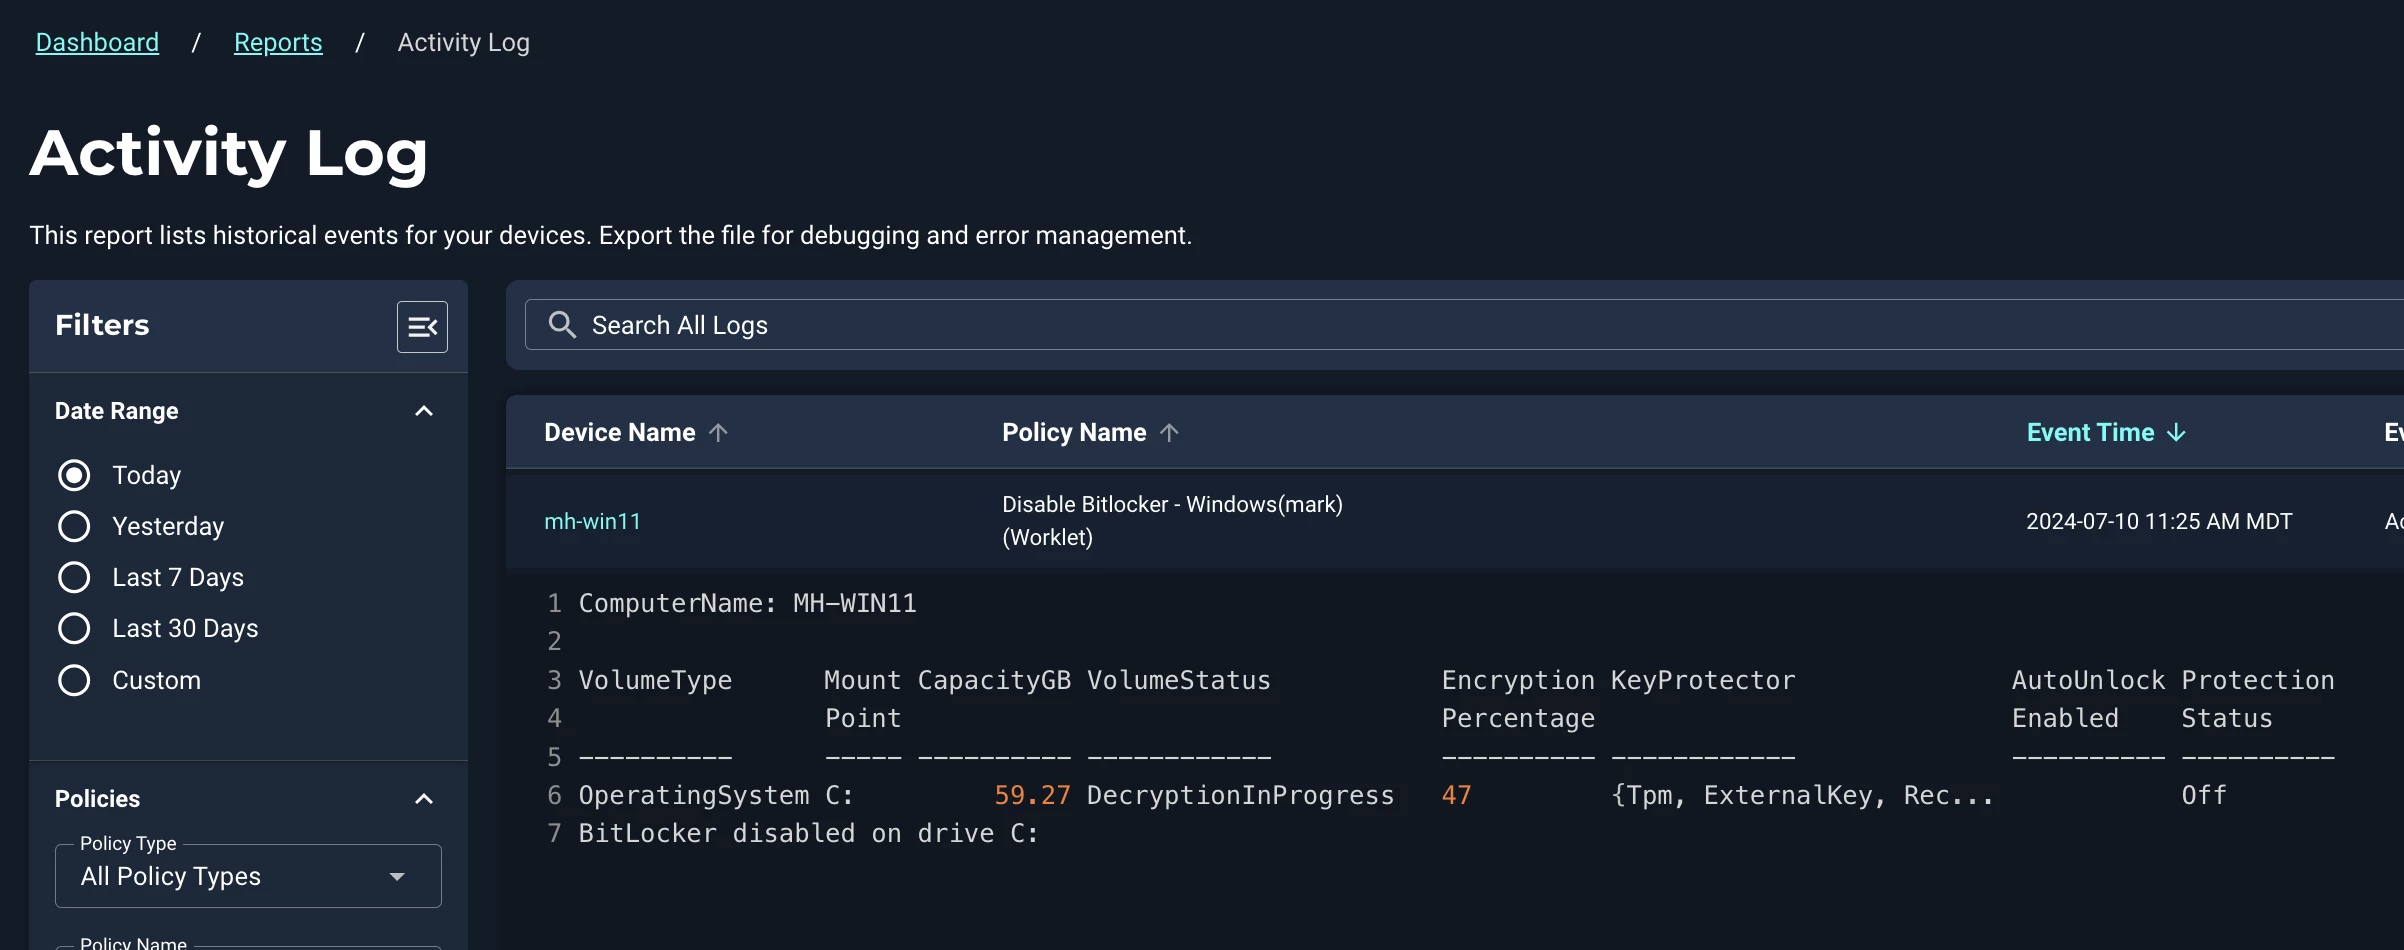
If a device is found to contain an encrypted drive, run the Remediation code and decrypt it (thanks OTTO):
 

powershell11 lines
# ======================
# Otto AI Generated Code
# ======================
# Get all BitLocker enabled drives
$bitlockerDrives = Get-BitLockerVolume | Where-Object {$_.ProtectionStatus -eq 'On'}

# Disable BitLocker on each drive
foreach ($drive in $bitlockerDrives) {
    Disable-BitLocker -MountPoint $drive.MountPoint -Confirm:$false
    Write-Output "BitLocker disabled on drive $($drive.MountPoint)"
}


Automox will take care of handling bitlocker during updates. You won’t have to disable/re-enable bitlocker around patch policies.