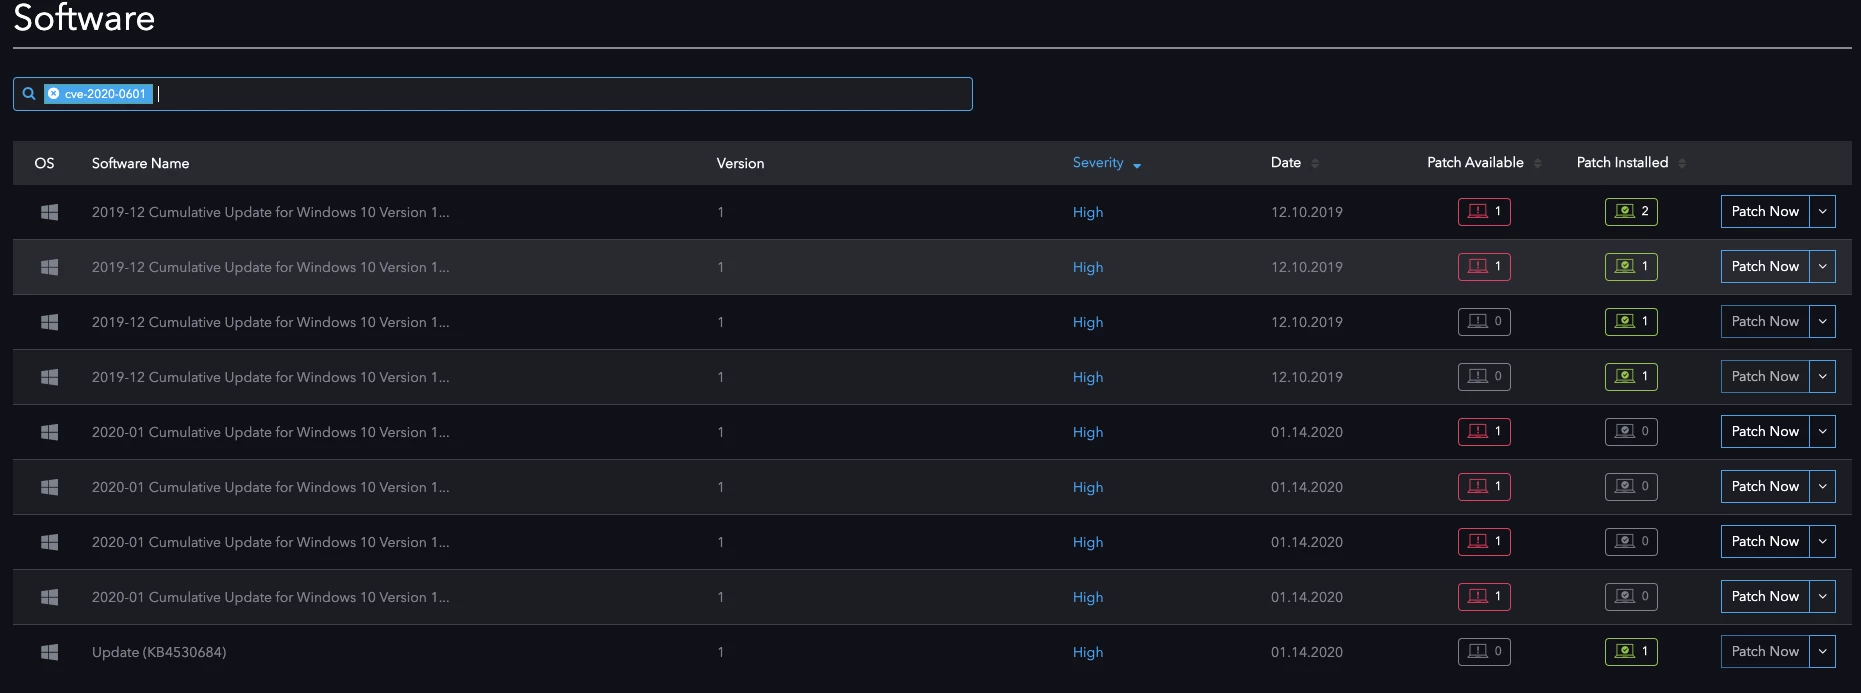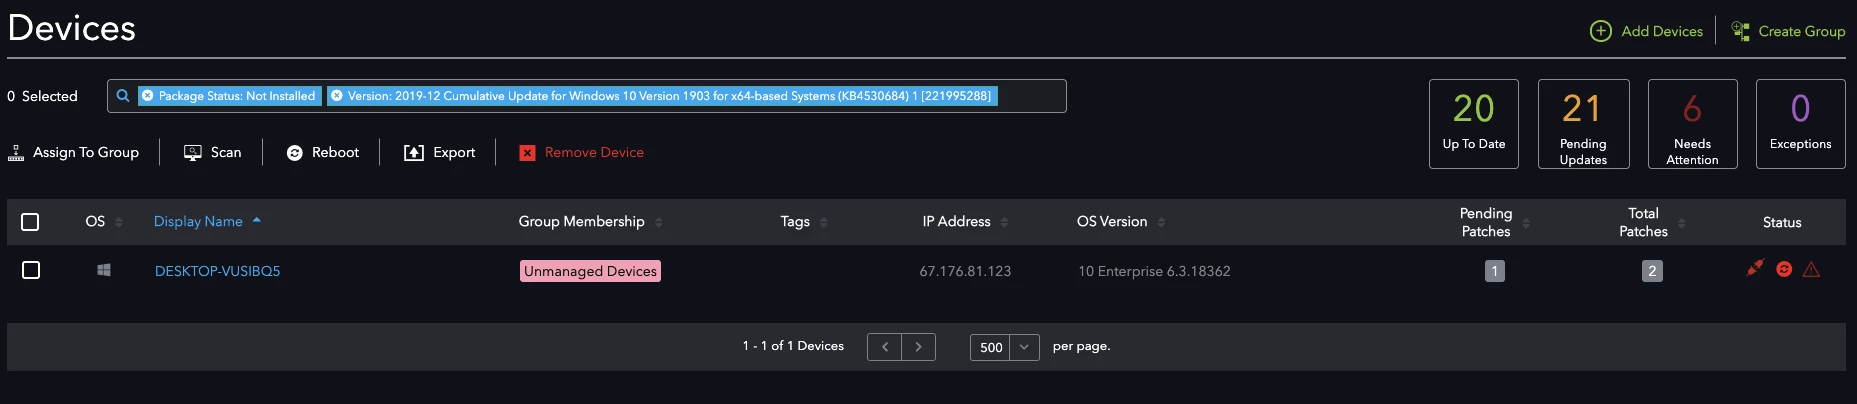
Hi all, following the recent announcement regarding CVE-2020-0601, one of our clients has requested a report on all our systems identifying which devices are vulnerable. Is it possible to generate such a report from Automox yet? That would be awesome!
This discussion is archived and closed to replies. Continue it in the Automox Community Slack.
Discuss on Slack